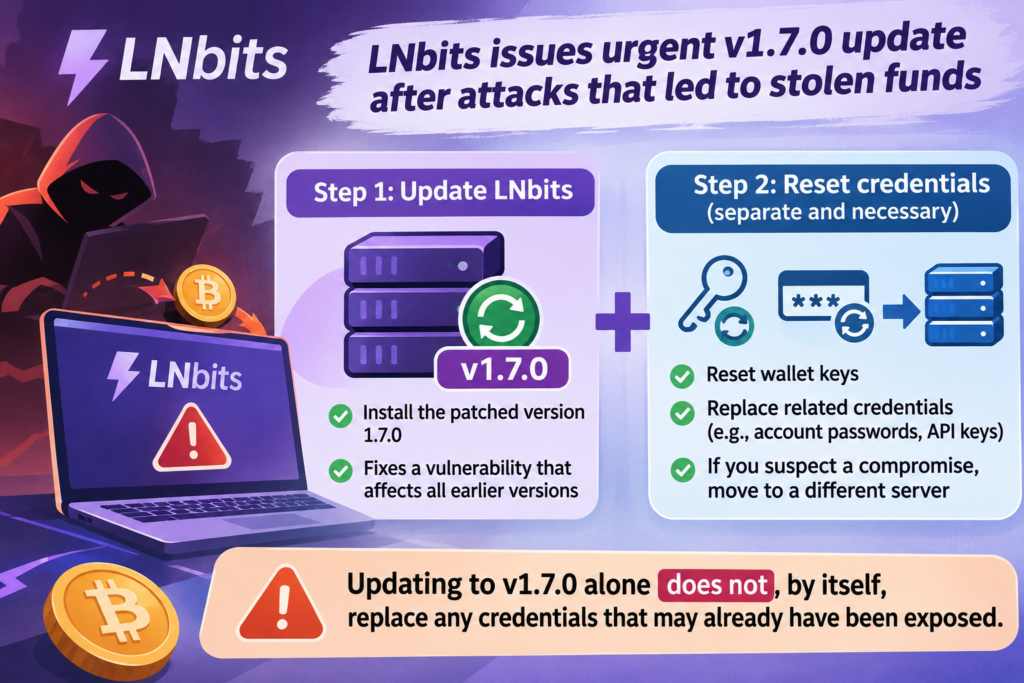
ChainCatcher reported on November 11, 2026, at 09:28 (UTC+8), citing Cointelegraph, that Lightning wallet platform LNbits had urgently released version 1.7.0 after a wave of attacks that resulted in stolen funds. LNbits urged users to update, warning that the vulnerability affects all earlier versions.
The update alone may not protect users whose credentials have already been exposed. LNbits advised users to reset wallet keys, replace related credentials and, if they suspect a compromise, move to a different server. These are separate steps: installing the patch does not revoke credentials an attacker may already have.
LNbits founder Ben Arc said the team was working to respond after users and the team suffered losses. Separately, one user reported that an attacker created a new account through the user’s LNbits instance and stole approximately 0.023 BTC. That account of the attack is the user’s report, not a confirmed description of every affected instance.